Federated Authentication Apple Business Manager: Complete Setup and Security Guide
Published August 24, 2026 · Updated September 7, 2026
Managing Apple devices at scale is not only about buying Macs, iPhones, or iPads. Organizations also need a secure way to create user identities, control access, assign devices, and keep accounts aligned with employee lifecycle changes. That is where federated authentication apple business manager becomes valuable.
With federation, employees can use their existing organization identity—typically a Microsoft Entra ID account to sign in to Apple services through a Managed Apple Account. Instead of creating and maintaining a separate password for Apple, the organization can use its existing identity provider as the source for authentication.
For IT teams, federated authentication apple business manager can reduce account-management overhead, support stronger access controls, and create a clearer separation between personal Apple Accounts and company-owned identities. However, it must be planned carefully. Domain conflicts, unmanaged Apple Accounts, directory sync settings, and administrator access can all affect the rollout.
This guide explains how federated authentication apple business manager works, what it does not do, how to prepare your domain, and how to deploy it safely with Microsoft Entra ID.
1. What Federated Authentication Means in Apple Business Manager
Federated authentication apple business manager is a sign-in model that links your organization’s verified email domain to an identity provider, such as Microsoft Entra ID or Google Workspace. Users then authenticate with their existing work credentials when they access supported Apple services using a Managed Apple Account.
A Managed Apple Account is an organization-owned identity created and controlled through Apple Business Manager. It can be used for Apple business services, assigned devices, Shared iPad, and iCloud access under the organization’s policies and identity rules.
The key idea is simple: Apple Business Manager does not need to become your main directory. Instead, federated authentication apple business manager lets your existing identity provider remain responsible for user authentication.
For example, an employee may sign in with:
Their password verification and multi-factor authentication request happen through Microsoft Entra ID. Apple receives the information needed to validate access, but the employee’s Entra ID password is not managed inside Apple Business Manager.
This setup helps organizations create a consistent login experience across Microsoft services, Apple devices, and enterprise applications.
Download Authenticator App
Secure your accounts with fast, reliable two-factor authentication. Download now and protect your login in seconds.
2. What Apple Business Manager Does for Organizations
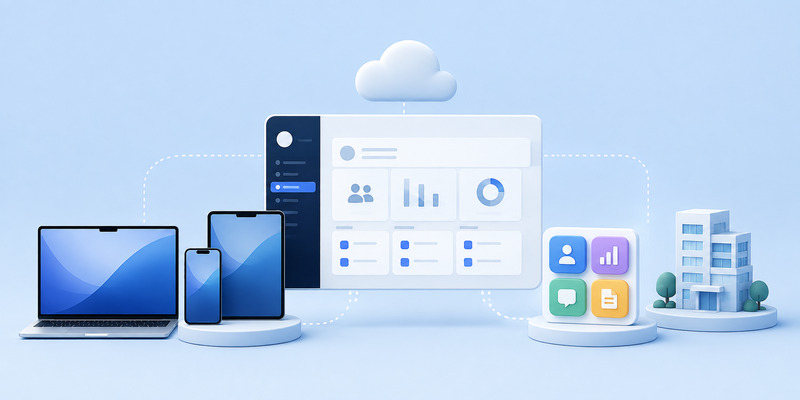
Many administrators first ask, what does apple business manager do? Apple Business Manager is Apple’s web-based portal for organizations that buy, deploy, and manage Apple hardware and business content.
It provides a central place to:
- Register or add organization-owned Apple devices.
- Assign devices to a device management service.
- Create Managed Apple Accounts.
- Connect an identity provider.
- Configure federation and directory sync.
- Buy and assign app licenses.
- Manage organizational locations and device suppliers.
- Prepare devices for automated enrollment.
The most important point is that Apple Business Manager is an ownership, enrollment, identity, and app-license platform. It is not designed to replace a full endpoint-management system.
The core apple business manager features help IT teams manage the business relationship between users, devices, apps, and Apple services. Federation is one of the strongest identity features because it allows staff to use familiar corporate credentials instead of handling a separate Apple password.
When teams ask what can apple business manager do, the answer includes much more than federated identity. It also supports Automated Device Enrollment, Apps and Books licensing, device assignment, organizational structure, and Managed Apple Account administration.
Still, federated authentication apple business manager is often the foundation for companies that want a more controlled Apple identity experience.
💡 Discover Helpful Guides: Apple TV 2 Factor Authentication: How to Fix Authentication Required on Apple TV
3. How Federated Authentication Apple Business Manager Works
The federated authentication apple business manager process begins with a verified organization domain. For example, if your company owns yourcompany.com, Apple must confirm that the organization controls that domain before federation can be enabled.
After verification, an administrator connects Apple Business Manager to an identity provider. In many environments, that provider is Microsoft Entra ID, previously known as Azure Active Directory.
This is why administrators may search for apple business manager federated authentication azure ad. The feature supports Microsoft Entra ID through OpenID Connect, allowing Apple Business Manager to trust the organization’s Microsoft identity environment.
The general flow looks like this:
- The organization verifies its domain in Apple Business Manager.
- A qualified Microsoft Entra ID administrator approves the connection.
- Apple Business Manager checks the domain and potential account conflicts.
- IT tests federation with a limited user account.
- Federation is enabled for the chosen domain.
- The organization can optionally configure directory sync.
Once active, users with a Managed Apple Account can authenticate through the connected identity provider. Password policies, conditional access requirements, and two-factor authentication are managed primarily in the identity provider.
This does not mean every Apple feature behaves exactly like a personal Apple Account. Managed Apple Accounts are organization-focused identities with specific service availability and control boundaries. IT should review the services their employees need before full rollout.
💡 Discover Helpful Guides: Changing Two Factor Authentication Apple: What You Need to Know
4. Requirements Before You Configure Federation
Before enabling federated authentication apple business manager, prepare the environment carefully. The technical connection itself is often straightforward; the account and domain decisions are usually the more difficult part.
First, confirm you control the domain you want to federate. Apple Business Manager requires domain verification. If you have multiple domains, decide whether all domains should be federated or whether you need a phased rollout.
Second, identify the correct Apple Business Manager administrator. The person configuring federation needs the necessary Apple Business Manager permissions. They should not rely on a personal Apple Account for critical administration.
Third, prepare an eligible Microsoft Entra ID administrator. Apple’s setup process requires approval from a Microsoft Entra ID Global Administrator when establishing the initial trust relationship. After setup, role requirements may be adjusted according to your organization’s access model.
Fourth, audit account usage. Employees may already have personal Apple Accounts that use their work email address. This is one of the most important considerations in federated authentication apple business manager.
When you federate a domain, users cannot continue creating new unmanaged Apple Accounts with that domain. Existing users with personal Apple Accounts tied to the domain may need to update their email address or take action during the transition process.
Finally, keep break-glass administrator accounts available. Federation administrators should have documented recovery methods and more than one authorized admin. Avoid building a setup where one unavailable person can block access to Apple Business Manager.
💡 Discover Helpful Guides: Apple Authenticator: Complete Guide to 2FA, Verification Codes & Apple Devices
5. Step-by-Step Setup With Microsoft Entra ID
A successful federated authentication apple business manager rollout should follow a staged approach rather than turning on federation for every employee immediately.
Step 1: Verify the organization domain
Sign in to Apple Business Manager and open the domain settings. Add your company email domain and complete Apple’s verification process. This usually involves adding a DNS TXT record through your domain registrar or DNS provider.
Do not proceed until the domain is verified. DNS verification proves the organization controls the domain and prevents another party from claiming it.
Step 2: Review existing Apple Account usage
Download or review the list of unmanaged Apple Accounts associated with the domain, if available in your Apple Business Manager environment. This helps identify employees who may be using work email addresses for personal Apple services.
Communicate early with affected users. They may need to change the primary email address on their personal Apple Account to a non-work email address. Clear communication helps prevent confusion when federation begins.
Step 3: Start the Entra ID connection
In Apple Business Manager, go to the domain and identity settings, then select the option to connect Microsoft Entra ID. The Entra ID Global Administrator signs in and grants the requested permissions on behalf of the organization.
The connection allows Apple Business Manager to read specific directory and authentication-related information needed for federation and, where configured, directory syncing.
The phrase apple business manager federated authentication azure ad remains common in older documentation and search queries, but Microsoft Entra ID is the current name for the platform.
Step 4: Review consent and permissions
Do not treat consent as a formality. Your Microsoft administrator should review what information Apple Business Manager can access and why. The permissions may include details necessary for domain reading, directory information, and security-related events.
This review should involve both identity and security stakeholders, especially in organizations with strict compliance requirements.
Step 5: Test with one user
A pilot is essential for federated authentication apple business manager. Choose a low-risk test user who has a valid corporate identity and understands that they are participating in the pilot.
Test the sign-in experience on the expected Apple device types. Confirm that the user can authenticate, that multi-factor authentication works as expected, and that account naming follows your chosen Managed Apple Account format.
Do not use your only Apple Business Manager administrator as the test identity.
Step 6: Turn on federation for the domain
After the test succeeds and conflicts are resolved, enable federation for the domain. From this point, the domain becomes linked to the identity provider for Managed Apple Account sign-in.
If the organization needs directory sync, configure it separately and validate attribute mapping before applying it broadly.
💡 Discover Helpful Guides: Microsoft Authenticator Apple Guide for iPhone
6. Handle Managed Apple Account and Domain Conflicts
Account conflict management is the part of federated authentication apple business manager that deserves the most planning.
A conflict occurs when a work email domain is already being used by a personal, unmanaged Apple Account. For example, an employee may have created a personal Apple Account years earlier using their company email address.
The account may contain personal photos, purchases, subscriptions, or iCloud content. IT should never assume it can simply take over that account. Personal Apple Accounts and Managed Apple Accounts are different identity types with different ownership and privacy expectations.
A careful rollout should include:
- An inventory of users with personal Apple Accounts on the work domain.
- A timeline for changing personal Apple Account email addresses.
- Clear employee instructions and support contacts.
- A communications plan before and after federation.
- Documentation for new hires and device onboarding.
The purpose of federation is not to access employees’ personal Apple data. The purpose is to prevent company domains from being used for newly created unmanaged accounts and to establish organization-controlled identities for work use.
When this step is ignored, federated authentication apple business manager can create unnecessary user frustration and help-desk tickets.
📖 Explore Articles: Best Authenticator App for Apple: Top Choices for iPhone, iPad, and Mac
7. Federation, Directory Sync, and MDM: What Is Different?
A frequent question is: is apple business manager an mdm? No. Apple Business Manager is not, by itself, a full mobile device management platform.
Apple Business Manager can assign organization-owned devices to a device management service, but it does not replace the policy, configuration, security, and deployment functions of an MDM platform.
An MDM can typically enforce settings such as:
- Passcode requirements.
- FileVault or encryption settings.
- Wi-Fi and VPN configurations.
- App installation and removal.
- Security restrictions.
- OS update policies.
- Device compliance reporting.
- Remote lock and erase actions.
Apple Business Manager supports the enrollment and assignment side of the workflow. Your MDM then manages the operational device policies.
So, do you need an mdm for apple business manager? Not always. Smaller organizations can use Apple Business Manager for device ownership records, Managed Apple Accounts, apps, and basic workflows. Apple also offers a built-in device management service in supported environments.
However, most organizations that need advanced policy control, compliance visibility, software deployment, and lifecycle automation will benefit from an MDM or another supported device management service.
Federation is also separate from directory sync:
- Federation controls where users authenticate.
- Directory sync creates or updates user account information from your identity provider.
- MDM manages the enrolled devices and applies configurations.
Understanding these boundaries helps teams design a cleaner Apple management architecture.
🗺️ Browse How-To Guides: Secondary Authentication Apple ID: Codes, Devices, and Recovery
8. Security, MFA, and Operational Best Practices
A strong federated authentication apple business manager deployment should use the same security discipline as any other identity integration.
First, enforce multi-factor authentication in Microsoft Entra ID. Apple supports the use of the identity provider’s authentication process, including two-factor authentication. Your company should decide which MFA methods are acceptable, such as passwordless sign-in, hardware security keys, number matching, or an approved authenticator app.
Second, apply least privilege. Use the minimum Apple Business Manager and Entra ID permissions needed for setup and ongoing management. Keep a documented list of who can manage domains, identity providers, directory sync, and device assignment.
Third, protect administrator accounts. Use separate administrative identities where practical, enforce MFA, and maintain at least two trusted administrators. Create and test recovery procedures before the organization depends on federation.
Fourth, pilot before scaling. Test with users from different departments and device types. Include a Mac, iPhone, iPad, and Shared iPad scenario when relevant to your environment.
Fifth, align offboarding processes. When an employee leaves, the organization should have clear ownership rules for their Managed Apple Account, assigned devices, app licenses, and business data.
Finally, document exceptions. Some departments may need different account formats, different domains, or special access to Apple services. Documenting these decisions prevents inconsistent manual work later.
 Find the Right Guide: Apple TV 2 Factor Authentication: How to Fix Authentication Required on Apple TV
9. How to Disconnect or Remove Federated Authentication
There may be situations where an organization needs apple business manager remove federated authentication from a domain. For example, the company may be changing identity providers, selling a business unit, restructuring domains, or correcting an early configuration decision.
Disconnecting federation should be treated as a planned identity change, not a quick troubleshooting step.
Before you disconnect federation:
- Identify every user who relies on federated sign-in.
- Confirm how Managed Apple Account passwords and access will be handled afterward.
- Review directory sync dependencies.
- Check device and Shared iPad workflows.
- Notify users of expected sign-in changes.
- Keep recovery-capable administrators available.
- Test the change with a limited scope where possible.
The exact steps to remove federation are available in Apple Business Manager’s domain settings. However, the operational impact depends on your current account configuration. Always review Apple’s current administrative guidance before making production changes.
For most organizations, federated authentication apple business manager should only be disconnected when there is a documented migration plan and clear responsibility between Apple, identity, endpoint, and help-desk teams.
10. Common Problems and Troubleshooting
Users cannot sign in after federation is enabled
Check whether the user belongs to the federated domain and has the expected identity-provider account. Confirm that the user is using the correct corporate username and that their Entra ID account is active.
Also verify that the user is attempting to sign in with a Managed Apple Account, not a separate personal Apple Account.
The Microsoft administrator cannot approve the connection
Confirm that the person signing in has the required Microsoft Entra ID Global Administrator role for the initial approval. Check whether conditional access policies, login restrictions, or consent policies are blocking the authorization flow.
Existing users have personal Apple Accounts on the domain
This is a domain conflict issue, not necessarily a technical federation failure. Follow the account-transition process and give users clear instructions to update the email address associated with their personal Apple Account.
Directory sync creates unexpected results
Review the source attributes, naming format, and user scope. Start with a small pilot group and avoid syncing the entire directory before validating the results.
MFA behaves differently than expected
MFA is controlled by your identity provider policy. Check Microsoft Entra ID conditional access, authentication methods, and sign-in logs. The issue may be in identity policy rather than Apple Business Manager.
11. Frequently Asked Questions
Is federated authentication Apple Business Manager worth using?
For organizations that already use Microsoft Entra ID or Google Workspace, federated authentication apple business manager is usually worthwhile. It centralizes authentication around existing work credentials and reduces separate password management.
Does federation create Managed Apple Accounts automatically?
Federation controls authentication. User accounts may also require directory sync or manual creation, depending on the organization’s chosen workflow.
Can employees still use personal Apple Accounts?
Yes, employees can keep personal Apple Accounts, but organizations should avoid using company email domains for personal accounts after federation. Personal and work identities should remain separate.
Does Apple Business Manager replace Microsoft Entra ID?
No. Federated authentication with apple business manager connects Apple’s business environment to your identity provider. Microsoft Entra ID remains the main source for user authentication and related access policies.
Does Apple Business Manager replace MDM?
No. Apple Business Manager supports device enrollment, account management, and app licensing. An MDM provides deeper device configuration, policy enforcement, and operational management.
Can I turn federation off later?
Yes, but removing it requires planning. Review account access, password impact, directory sync, device use cases, and user communications before making changes.
12. Final Thoughts
Federated authentication apple business manager gives organizations a practical way to bring Apple identity management into an existing enterprise authentication strategy. It allows employees to use familiar corporate credentials while helping IT create controlled Managed Apple Accounts for business use.
The best results come from treating federation as an identity project, not just a device-management setting. Verify domains, audit existing personal Apple Accounts, test with a pilot group, secure administrator access, and define a clear support process before enabling it at scale.
When configured carefully, federated authentication apple business manager can simplify sign-in, strengthen access control, and make Apple deployments easier to manage across the organization.
Download Authenticator App
Secure your accounts with fast, reliable two-factor authentication. Download now and protect your login in seconds.